Keep external content at a distance.
Local Browser Isolation (LBI) keeps managed web work inside a local isolation boundary. A safe viewer is designed to let people inspect supported documents within that protected workflow.
01 AI Security Workspace
The device boundary for enterprise AI work.
Neurlect controls sensitive information movement through today’s human AI workflows—at the device boundary.
Local browser isolation. Safer document handling. Explainable controls.
Agent workflow controls are an architecture and expansion direction.
02 The operating reality
AI work brings external websites and documents into everyday workflows. The same workflows send prompts, files, and sensitive details back out.
Keep risky content in a protected environment. Evaluate sensitive information against the customer’s policy before it moves to the next step.
Preserve the workflow.Govern the movement.
03 The Neurlect boundary
Neurlect places policy at the device boundary of the Neurlect-managed workspace. The workflow stays familiar while the boundary evaluates sensitive movement and applies an allowed, protected, or blocked action before the next step.
Local Browser Isolation (LBI) keeps managed web work inside a local isolation boundary. A safe viewer is designed to let people inspect supported documents within that protected workflow.
For supported document paths, content disarm and reconstruction (CDR) is designed to remove potentially hazardous elements and reconstruct a usable document. Inspection, reconstruction, viewing, and export remain distinct steps; supported formats and release scope are checked during the demo.
Architecture illustration · product control flow
Synthetic work enters a managed context.
The user keeps a familiar AI workflow.
The local host evaluates movement before the next step.
The decision stays explicit and explainable.
The ledger records only what the device can support.
See how a synthetic work item moves through the workspace, a device policy, an illustrative action, and a local evidence relationship.
This architecture illustration describes the control flow. It does not establish that every protection or transformation path is available.
 Managed workspace
Local host
Prompt draft
Summarize the launch assumptions in this internal strategy note.
Synthetic document entered the managed workspace.
04 Connected controls
A local boundary for Neurlect-managed web work, designed to separate external content from the everyday work environment.
Protected contextSafe viewing and CDR address supported document paths. Inspection, reconstruction, viewing, and export remain distinct steps.
Inbound protectionCustomer-defined grades are intended to connect sensitive information to each customer’s controls. Customer-specific Block connections have been checked in synthetic workflows; end-to-end customer classification remains under validation.
Under validationMasking hides sensitive details. Pseudonymization replaces identifiers while preserving useful relationships within its defined scope. End-to-end customer pseudonymized transmission remains under validation: a policy permission to send does not establish that transformation or delivery occurred.
Under validationWhen an exact-content relationship is confirmed on the device, the local ledger records that connection. Otherwise, it reports relationship not established. Broader incident explanations remain under validation.
Exact-content foundation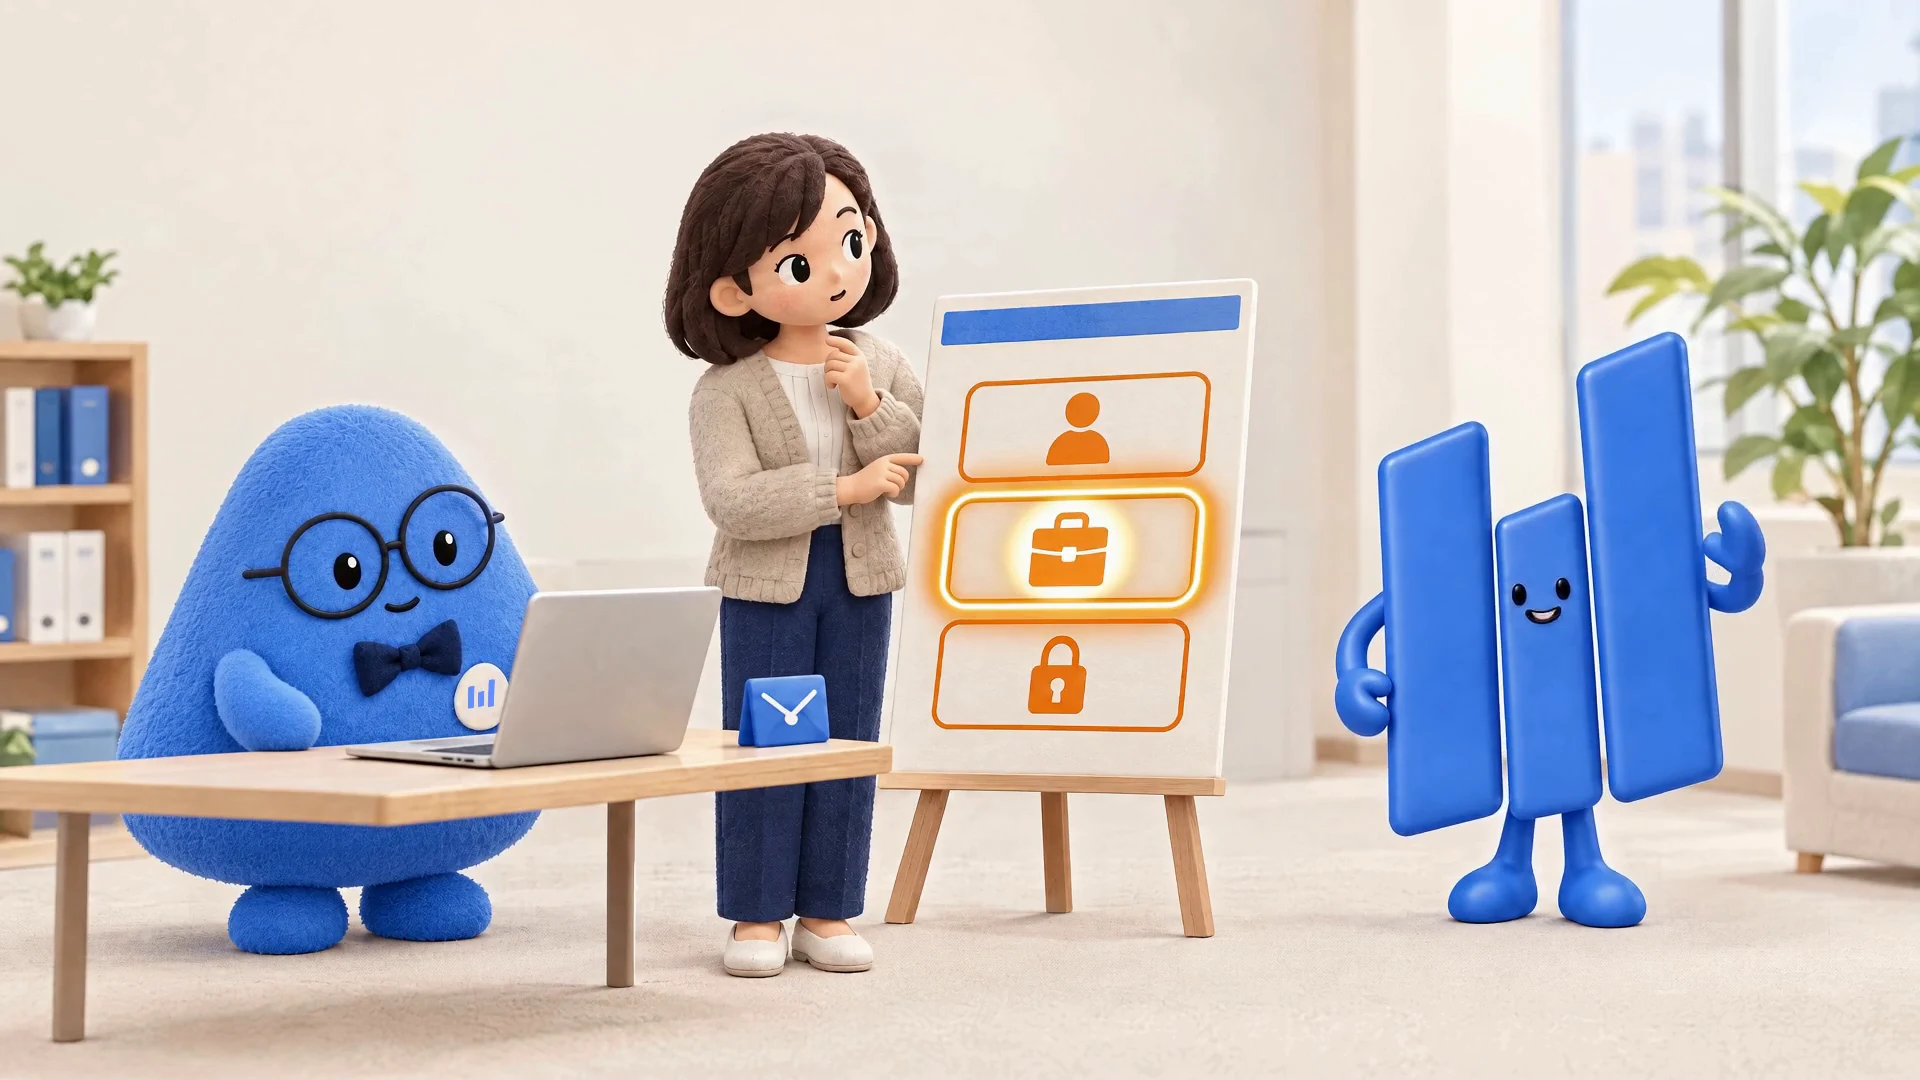
Personal details, business information, and confidential work need context. Customer-defined grades remain under validation; the illustrated symbols are not universal security levels.
05 Explainable by design
Neurlect separates what the device confirmed from what it could not establish, and separates relationship status from evidence acquisition and ledger integrity.
The interface does not turn missing evidence into a clean bill of health.
The wider record linking inspection policy, actual treatment, and input delivery remains under validation.
An input-delivery result is not proof that an AI service received it. For supported output, a recovered watermark can provide an investigation candidate; it is not proof of attribution.
An exact-content relationship was confirmed on the device.
The product did not establish the relationship. This does not mean no relationship exists.
Required comparison material was not acquired.
A recording loss, damage, or completeness issue was detected and disclosed.
These are separate axes, not four levels of certainty.
06 People now. Agents next.
Product foundation
Architecture direction
Agent controls are an architecture and expansion direction, not a representation of complete Agent Security functionality.
07 Privacy-minimized evidence
Neurlect’s architecture is designed to keep detailed content references and verification material in the customer environment while exposing privacy-minimized states and event relationships to management surfaces.
Management-plane coverage is being validated across requests, storage, responses, and logs. This principle is scoped to evidence architecture and is not a universal statement about all device data flows.
08 Controlled environments
Neurlect is designed for regulated and sensitive environments across financial services, public sector, research, and enterprise operations.
Policy stays anchored to the customer’s device boundary.
Detailed evidence remains under the customer’s control.
Relationship and ledger health never collapse into one claim.
Today’s human AI workflows establish a possible foundation for future governed agent actions.
09 Private demo
Request a private walkthrough of the workspace, device-boundary policy, and evidence model. We will use a synthetic workflow, not your sensitive data.